Category: Cyber-Psychology

  • Podcast Episode: Predatory Privacy And AI

    Podcast Episode: Predatory Privacy And AI

    // AI disclosure

    This whole episode is AI generated, Pip and Mara included. I got bored and played with the WordPress toys, and one of them plays with my literary work. Of course it’s confused and sycophantic. Regardless, it’s here for further insight into the Privacy’s Predatory Policy series.

    The next blog series, on AI-generated music, is coming in the next few weeks for the weekly blog. It might be weekly, but it might not be. Maybe it is, but likely it won’t be, because ADHD.

    Pip: Welcome to Deeez Nuuuts Consulting LLC™, where today's episode is brought to you by the forty-seven companies that already have your data from the last time you leased a couch.

    Mara: We are covering the architecture of data extraction, the psychology of manufactured consent, and — finally — a practical countermeasure stack for people who would like to be slightly more expensive to surveil.

    Pip: Let's start with how the trap is built and what you can actually do about it.

    —

    Privacy Extraction And Countermeasures

    Mara: The series we are recapping began with a rent-to-own application as a case study — not because furniture leasing is uniquely sinister, but because its data collection is unusually visible. The question across all three parts is: what does that paperwork actually authorize, why do people sign it anyway, and what can a person under real-world cognitive load actually do in response?

    Pip: Part 1, covered in Predatory Privacy Policies, establishes the intake form as a data asset. Income, residence history, references, a government ID scan — all of it feeding what the FTC called something specific.

    Mara: The Federal Trade Commission's foundational report documented that "consumer-finance application data is among the most commercially valuable categories of personal information precisely because it links identity, location, employment, and financial behavior in a single verified record."

    Pip: One verified record. That is the thing being sold. The couch is almost incidental.

    Mara: And the sharing language in published policies makes the downstream flow nearly unlimited. Rent-A-Center's own cookie disclosure names twelve advertising partners by name — Meta, Google, TikTok, Pinterest, Yahoo, Microsoft Bing, Pandora, Zeta, AppNexus/Xandr, Verizon/Oath, Causal IQ, and Claritas. Twelve companies watching one rental application.

    Pip: Part 2 — also titled Privacy's Predatory Policy — explains why people sign anyway. The answer is cognitive load, and it turns out financial scarcity alone reduces available deliberative bandwidth by roughly thirteen IQ points. The brain is already running on fumes by the time the policy arrives.

    Mara: Which brings Part 3 to its central design constraint. The author is explicit: "no countermeasure in this stack is allowed to assume you have free time, legal training, or emotional slack."

    Pip: That constraint is doing real work. A defense that requires you to become a different person is not a defense.

    Mara: The six layers that follow are built around that limit. Triage four clause types in four minutes instead of reading fifty-five. Use email aliases and a VoIP number to starve the join key that links you across databases. Send deletion requests even if your state has no privacy law, because the economics of compliance pipelines often mean companies honor them anyway.

    Pip: Turn on Global Privacy Control — one browser setting, legally mandatory in roughly a dozen states, already backed by multimillion-dollar enforcement actions.

    Mara: And the layer the author calls the existential core: obfuscation. Brunton and Nissenbaum describe it as the deliberate production of ambiguous or misleading signals to make surveillance data less valuable. Your loyalty card does not need your real birthday.

    Pip: The goal is not invisibility. The author is clear that hiding is unavailable. The goal is resolution degradation — converting yourself from a high-fidelity, cross-checked, monetizable record into something a marketer's model cannot confidently price.

    Mara: The final layer is the CFPB complaint database. Filing costs ten minutes. The company must respond within roughly fifteen days, and the complaint becomes a permanent public record that regulators and class-action attorneys mine for patterns. The author's framing: "You spent fifty-five minutes not reading their agreement. Spend ten minutes writing your own entry in the public record."

    Pip: The whole series started because a rent-to-own application the author signed years ago is still echoing through a family member's voicemail. The countermeasure stack cannot unsign that. What it changes is the price of the next extraction attempt.

    Mara: And that segues to a thread running quietly through all three posts — the author used multiple LLMs as a literary assistant throughout the series, which raises its own questions about what we hand to machines while writing about what machines do with what we hand them.

    —

    AI Writing And Literary Assistants

    Mara: Part 2 of the series opens with a disclosure that sits a little uncomfortably next to its subject matter: "Literary assistant = several fuckin' LLMs all set to some deep philosophical and intrinsical thought model."

    Pip: A series about the cost of handing your data to systems you cannot audit, drafted with the help of systems you cannot audit. The author noticed. That is probably the point.

    Mara: Part 1 carries the same note. The question the series implicitly leaves open is whether AI-assisted writing changes what the reader is actually reading — and whether that matters differently when the topic is surveillance.

    —


    Pip: The substrate economy runs on friction being low and awareness being lower. The series makes both of those more expensive.

    Mara: Same blade, other edge — the author's phrase for it. The reason the treatment post was ten weeks late is the same reason the treatment is necessary.

  • Privacy’s Predatory Policy

    Privacy’s Predatory Policy


    Part 3: The Countermeasure Stack

    This is the final installment of a three-part series. Part 1 mapped the architecture of extraction — what gets collected, where it flows, what “vendors, service providers, affiliates, and partners” actually authorize. Or maybe it had nothing to do with any of that shit at all and was more or less an informative report on the ways that companies “Get ya.”

    Part 2 examined why the architecture works: consent manufactured under cognitive load, financial scarcity, and decision environments engineered for compliance.

    Part 3 is the countermeasure stack, hopefully… the one that takes the actual effort of staying on topic. Let’s see how this goes. And yes, this is a really fuckin super late submission. I’ll tell you why — because the reason is the thesis. Pay attention to how the reason for something can also be another edge of the same blade. You’ll see.

    What this post is and what it isn’t

    Consumer education and structural commentary. Not legal advice, not an accusation against any specific company. Where companies, statutes, or documents are referenced, they appear as examples of industry-wide patterns, and any reader is encouraged to verify current practices and current law directly, noting the date of access. Laws cited below vary by state and change frequently.

    The ten-week confession

    Here’s the reason, as promised. I run a consulting practice, produce a podcast, parent two teenagers alone, and am finishing a graduate degree in machine learning. I wrote Part 2 — the one about how cognitive load converts deliberation into heuristic compliance — and then I did not write Part 3 for ten weeks, because my cognitive load converted deliberation into heuristic compliance. The diagnosis post was written because the diagnosis is downhill. The treatment post stalled because treatment requires exactly the resource the system is designed to deplete: surplus bandwidth. That’s not an excuse. That’s a replication study with an n of 1. Same blade, other edge.

    So here is the design constraint for everything below: no countermeasure in this stack is allowed to assume you have free time, legal training, or emotional slack. Part 2 established that those assumptions are what make the trap work. A defense that requires you to become a different person is not a defense. It’s a second trap with better branding.

    One more thing before the stack. None of this gets you out. There is no out. You cannot un-exist from the substrate economy — Zuboff (2019) is right that participation in modern life is participation in extraction. What you can change is your resolution. The system doesn’t need you to disappear to lose interest in you. It needs you to become expensive to process. Every layer below has one function: raise the cost of extracting you until the math stops working in their favor.

    You cannot opt out of existing. You can opt out of being legible.


    Layer 1: The Four-Sentence Scan // read 4 minutes, not 55

    Part 2 established that reading the whole policy is structurally impossible — 55 minutes for one Microsoft agreement, 200+ hours per year across all services (McDonald & Cranor, 2008). The mandated-disclosure model failed categorically (Ben-Shahar & Schneider, 2014). Fine. Stop trying to read policies. Start triaging them.

    Four clause types carry almost all of the load. Ctrl+F them. Four minutes, not fifty-five:

    1. The arbitration clause. Search “arbitration,” “class action,” “waiver.” This tells you whether you can ever sue them, alone or together. Usually the answer is no, and usually there’s a 30–60 day window to opt out of arbitration by mail after signing — a right almost nobody exercises because almost nobody knows it exists. [Side note: they buried your one procedural weapon in a clause about giving up your procedural weapons. Respect the craft, hate the craftsman.]
    2. The sharing sentence. Search “affiliates,” “partners,” “third parties.” Part 1 covered this — it’s the sentence that authorizes everything, including entities that don’t exist yet.
    3. The modification clause. Search “modify,” “changes,” “continued use.” This is the clause that makes every other clause temporary. Whatever you agreed to is a draft.
    4. The corpse clause. Search “bankruptcy,” “merger,” “sale of assets.” This is where your data becomes inventory if the company dies or gets eaten.

    Those four searches tell you 90% of what the document does to you. This is not full informed consent — Part 2 proved that’s not on the menu. It is consent with your eyes open instead of taped shut, performed at a cognitive price point a person under load can actually pay.

    Layer 2: Reference Firewalling // stop donating your family to the machine

    Part 1 told you about my older sister’s voicemail box — the one that spent years absorbing colorful two-minute messages from debt collectors hunting me through the references I’d handed over to lease furniture. I gave the machine her number. The machine never gave it back. That’s not a bug in my past; that’s a permanent edge in a graph database, and I drew it myself.

    So: compartmentalize what you feed the intake form.

    • Email: use aliasing (most modern email providers and several dedicated services offer per-service addresses). One service, one alias. When the spam starts, the alias tells you exactly who sold you, and killing the alias kills the channel.
    • Phone: a VoIP number for applications, sign-ups, and retail is one of the highest-yield moves in this entire stack. Your real number is a join key — the field that lets a hundred databases confirm they’re all describing the same person. Starve the join.
    • References: if an application demands personal references, understand what you’re doing — you are entering people who never consented into a skip-tracing network. Warn them. Better: use contacts who’ve agreed to play goalie. And know the boundary line — under the Fair Debt Collection Practices Act, collectors may contact third parties essentially only to locate you, generally may not reveal the debt, and generally may not contact the same third party repeatedly (Fair Debt Collection Practices Act, 1977). What happened to my sister’s voicemail had a statute against it the whole time. Nobody in that transaction was ever going to tell either of us.

    The existential note here is quiet but real: the data you surrender is rarely just yours. Every reference, every synced contact list, every “find my friends” toggle is you spending other people’s privacy as currency. The substrate economy runs on that ambient betrayal being frictionless. Add friction.

    Layer 3: The Statute Stack // rights you already own and never invoice

    As of this writing, roughly 20 states have comprehensive consumer privacy laws in effect, granting some mix of access, deletion, correction, and opt-out-of-sale rights, with enforcement now resulting in seven- and even ten-figure penalties. Consumer privacy enforcement is no longer theoretical; verify your state’s current status, because this map redraws itself annually.

    Here’s the part that matters if, like me, you live outside that map: companies frequently honor deletion and opt-out requests nationally because maintaining fifty different compliance pipelines costs more than just processing your request. The law gives Californians the right. The economics often give it to you. Send the request anyway — the worst case is a form rejection, and the best case is a row deleted from a table you were never supposed to know existed.

    Illinois residents, we hold one weird ace: the Biometric Information Privacy Act (740 ILCS 14) — the strongest biometric law in the country, with a private right of action. Remember the ID-capture systems from Part 1 quietly harvesting biometric identifiers during rent-to-own applications? In Illinois, that harvesting has rules, written consent requirements, and teeth. Know which of your body parts your state protects. [Side note: that is a sentence I typed soberly, in a consumer finance article, in 2026. The field I work in is not okay.]

    Round it out with the Fair Credit Reporting Act: you have the right to dispute inaccurate information with both the furnisher and the credit bureaus, and they are legally required to investigate (Fair Credit Reporting Act, 1970). Disputes cost you a template letter. They cost the company a regulated workflow with deadlines. That asymmetry is the whole point of this layer.

    Layer 4: The Signal Layer // one browser setting with a statute behind it

    Cookie hygiene advice is usually theater — clear your cookies, feel virtuous, get re-fingerprinted in eleven milliseconds. Skip the theater. Do the two things with structure behind them:

    • Turn on Global Privacy Control. GPC is a browser-level signal that tells every site you visit “do not sell or share my data” — automatically, on every page load, forever (Global Privacy Control, n.d.). In roughly a dozen states, honoring that signal is now legally mandatory, and regulators have already extracted multimillion-dollar settlements from companies that ignored it. This is the rarest thing in privacy: a countermeasure that costs one browser setting and is backed by enforcement actions. It is the closest thing to a free lunch in this entire series.
    • Use a browser or extension stack that blocks third-party trackers by default. Part 1 counted twelve named advertising partners watching a single rental application. A tracker-blocking browser turns twelve witnesses into zero without you performing any ongoing labor. The best countermeasure is the one that works while you’re too tired to care, because Part 2 established that “too tired to care” is your default state by design.

    Layer 5: Obfuscation // become bad data

    Everything above focused on shrinking whatever leaves you in the first place — minimizing the data exhaust you emit at all. This layer works differently: it degrades what they think they already know.

    Brunton and Nissenbaum (2015) call it obfuscation: the deliberate production of ambiguous, misleading, or excessive signals to make surveillance data less valuable. It’s the privacy strategy of people who can’t realistically refuse data extraction — which, in modern consumer economies, is effectively everyone. Part 2 established that opting out is mostly a fantasy; systems you rely on to live and work demand data as the price of admission.

    Practically: your loyalty account doesn’t need your real birthday. The store demanding a phone number at checkout can have the VoIP one, or the classic (area code) 867-5309, which I’m told has racked up somebody an ungodly number of fuel points. Optional fields are optional. Forms that demand truth you’re not legally required to give can receive plausible noise instead — details that look realistic to a marketer but don’t uniquely and verifiably pin you down. The profile they compile becomes a portrait painted from a police sketch of a rumor.

    Understand what this layer actually is, because this is the existential core of the whole stack. You are not hiding. Hiding is unavailable. As Part 1 showed in the context of consumer-finance applications — where a single form ties together identity, employment, location, and behavior into one highly prized asset (Federal Trade Commission, 2014) — the value of data comes from its role as a verified, linkable record. Verified is the load-bearing word. You are lowering your resolution: converting yourself from a high-fidelity, cross-checked, monetizable record into a smeared, self-contradicting, low-confidence one. Break the verification, break the price.

    Individually, a fake birthday or a burner number seems trivial. Together, consistent layers of plausible noise break the clean lines that would otherwise connect one singular, verified you across databases and contexts. They don’t stop data from leaving; they change what that data can reliably say.

    [side note: obviously do not obfuscate on credit applications, government forms, or anything with a fraud statute or comparable legal obligation attached. This is a practical rule of thumb, not legal advice: where the law requires truth, give truth; where a marketing department merely prefers truth, give art — understanding that even art can sometimes have practical consequences, like account lockouts or lost perks.]

    Layer 6: The Complaint Weapon // ten of your minutes vs. their compliance department

    Last layer, most underused. The Consumer Financial Protection Bureau operates a public complaint database. When you file, the company is expected to respond, typically within about 15 days, and the complaint — including the company’s handling of it — becomes a permanent public record that regulators, journalists, and class-action attorneys mine for patterns (Consumer Financial Protection Bureau, n.d.). Your state attorney general runs a parallel channel, and in the twenty states, the AG is the privacy enforcer.

    Run the asymmetry math, because asymmetry is what this whole series has been about. Their side of the architecture works because your cost to resist is high and your individual value to them is low. A complaint inverts it: costs you ten minutes and a paragraph; costs them a tracked, deadlined, regulator-visible workflow. One complaint is a mosquito. A pattern of complaints is how enforcement priorities get set. The record producing those billion-dollar settlements didn’t materialize out of nowhere — it aggregated from individuals who spent 10 minutes.

    You spent fifty-five minutes not reading their agreement. Spend ten minutes writing your own entry in the public record. Make the paperwork flow uphill for once.


    The reckoning, itemized

    Six layers. Not one requires a law degree, a threat model, or a personality transplant. Triage the four sentences. Firewall your people. Invoke the statutes you already own. Flip the GPC switch. Degrade your resolution. File the complaint. Each one is small. Stacked, they change what kind of object you are in the dataset — from a verified, compliant, high-yield record into something noisy, self-aware, legally armed, and annoying to process.

    I started this series because a rent-to-own application I signed under exactly the conditions Part 2 describes is still echoing through my family’s phones years later. I can’t unsign it. Neither can you unsign yours. The substrate doesn’t offer refunds. What it offers — what it can’t help offering, because it’s made of math — is a price sensitivity. Extraction continues exactly as long as you’re cheap.

    So stop being cheap.

    Automatic consent made you compliant. Informed consent brought the reckoning. The reckoning is a checklist, and now you have it.

    References

    Ben-Shahar, O., & Schneider, C. E. (2014). More than you wanted to know: The failure of mandated disclosure. Princeton University Press.
    Biometric Information Privacy Act, 740 ILCS 14 (2008). https://www.ilga.gov/legislation/ilcs/ilcs3.asp?ActID=3004
    Brunton, F., & Nissenbaum, H. (2015). Obfuscation: A user’s guide for privacy and protest. MIT Press.
    Consumer Financial Protection Bureau. (n.d.). Submit a complaint. https://www.consumerfinance.gov/complaint/ [Accessed July 2, 2026]
    Fair Credit Reporting Act, 15 U.S.C. § 1681 et seq. (1970).
    Fair Debt Collection Practices Act, 15 U.S.C. § 1692 et seq. (1977).
    Federal Trade Commission. (2014). Data brokers: A call for transparency and accountability. https://www.ftc.gov/system/files/documents/reports/data-brokers-call-transparency-accountability-report-federal-trade-commission-may-2014/140527databrokerreport.pdf
    Global Privacy Control. (n.d.). Take control of your privacy. https://globalprivacycontrol.org/ [Accessed July 2, 2026]
    McDonald, A. M., & Cranor, L. F. (2008). The cost of reading privacy policies. I/S: A Journal of Law and Policy for the Information Society, 4(3), 543–568.
    Zuboff, S. (2019). The age of surveillance capitalism: The fight for a human future at the new frontier of power. PublicAffairs.
  • Privacy’s Predatory Policy

    Privacy’s Predatory Policy

    Part 2 of the series of the similar name, how much do you like to read?

    Literary assistant = several fuckin’ LLM’s all set to some deep philosophical & intrinsical thought model

    Part 2: The Cyberpsychology of “I Agree”


    55 minutes. 14,268 words. You didn’t read it. That’s the point.

    This is the second installment of a three-part series. Part 1 mapped the architecture of data extraction — what gets collected, where it goes, and what four sentences in a typical privacy policy actually authorize. This part examines why the architecture works: the cyberpsychology of consent under cognitive load, financial pressure, and decision environments engineered to produce compliance. Part 3 builds the countermeasure stack.

    What this post is and what it isn’t

    Consumer education and structural commentary. Not legal advice, not an accusation against any specific company. Where companies or documents are referenced, they appear as examples of industry-wide patterns, and any reader is encouraged to verify current practices directly.

    The 55-minute confession

    Microsoft’s consumer Services Agreement — the contract governing Outlook, Xbox, Copilot, Teams, OneDrive, and over a hundred other products — opens with an unusual disclosure. At the top of the document, before any substantive clause, the company prints an estimated reading time: 55 minutes (Microsoft Corporation, 2025). The document contains 14,268 words.
    For context, that is longer than most of the academic papers cited in this series.

    The company is not hiding the length. It is advertising it.
    That disclosure functions as a liability shield:
    we told you how long it would take; you chose not to read it.

    The document then proceeds to contain a binding arbitration clause and class action waiver (Section 15), a liability cap of $10 for free services (Section 13), [*side note*: I remember reading that for the first time and chuckling about how important money is to people that have it, and how important it is to keep money from the people who are somehow hurt by a companies negligence or salience that something is prone to fucked upedness, and that I’m sure they have a quarterly acceptable loss allowed in the risk assessment matrix, but anyway i digress] broad rights to modify terms unilaterally with continued use constituting acceptance (Section 7), the right to process and store all inputs and outputs to AI services for monitoring (Section 14.s.v), and the right to terminate services and delete user content at any time (Section 4.a.iv).

    Every one of those clauses has measurable legal and financial consequences for the user. None of them is readable at the moment of signing.

    This is not a failure of the system.
    It is the system working as designed.

    The impossibility of reading: a quantified problem

    The scale of the consent problem is not rhetorical. It has been measured. Ben-Shahar and Schneider (2014), in their foundational study of mandated disclosure regimes, calculated the aggregate reading burden that privacy policies impose on consumers. If an average American internet user attempted to read every privacy policy they encountered in a year, the total time cost would exceed 200 hours — approximately five full workweeks (McDonald & Cranor, 2008). That estimate was published in 2008. The number of services, apps, and platforms requiring consent has increased by an order of magnitude since then.

    The problem is not that people are lazy. The problem is that the reading demand is structurally impossible to satisfy. No human being has the time, cognitive bandwidth, or legal training to process the volume of consent documents the digital economy generates. The notice-and-choice framework — the legal architecture that treats “I Agree” as meaningful consent — is built on a fiction: the fiction that a reasonable person reads, comprehends, and meaningfully evaluates the terms before clicking.

    Solove (2013) named this the failure of privacy self-management: the regulatory model asks individuals to manage their own privacy through individual consent decisions, while generating a volume and complexity of decisions that no individual can manage. The model does not fail occasionally. It fails categorically, by design, for every user, every time.

    Cognitive load: why the brain says “yes” when the answer should be “wait”

    The psychological mechanism is well-documented and operates at a level below conscious deliberation.
    Human decision-making under cognitive load follows predictable patterns. When working memory is saturated — by time pressure, financial stress, information overload, or emotional arousal — the brain shifts from deliberative processing (slow, analytical, effortful) to heuristic processing (fast, intuitive, error-prone). Kahneman (2011) describes this as the shift from System 2 to System 1 thinking. In the context of privacy decisions, this means the user defaults to simple heuristics: “everyone else agreed, so it must be fine”; “this company is well-known, so they must be trustworthy”; “I need this service right now, and reading the policy won’t change anything.”

    Acquisti, Brandimarte, and Loewenstein (2015) documented this pattern specifically in privacy behavior, identifying three structural properties that make privacy decisions systematically irrational: information asymmetry (the company knows what the data is worth; the consumer does not), the abstract and probabilistic nature of privacy harms (the damage is future, uncertain, and difficult to trace to any single disclosure), and context dependence (the same person will share or withhold the same information depending on how the choice is framed).

    The moment of consent in a rent-to-own store combines all three. The customer is under financial pressure, time pressure, and emotional arousal (that suggestive term just means it’s some shit that you know you need). The privacy policy is long, legalistic, and presented at the exact moment the customer’s cognitive bandwidth is occupied by a different decision: Can I afford this payment schedule? The heuristic kicks in. The box gets checked.

    The machine that builds your “yes”

    No choice is presented neutrally. Thaler and Sunstein (2008) named this choice architecture — the recognition that the entity structuring a decision shapes its outcome more powerfully than the decision’s content.
    Default settings, visual hierarchy, friction distribution — these are not neutral design choices; they are behavioral instruments.

    Brignull (2023) cataloged the digital versions: pre-checked consent boxes, double-negative opt-outs, single-click acceptance versus multi-screen resistance. The pattern is straightforward — reaching an agreement happens easily, but understanding each other takes effort, and the imbalance is intentionally designed.

    In a rent-to-own store, the conversion funnel is analog, but the exploit is identical. The raw, unprotected privacy policy sits between the legs of the customer and the merchandise. Every design incentive minimizes the time spent on the policy and maximizes the speed to signature. The document is technically available. It is positionally invisible. Calo (2014) calls this digital market manipulation — the systematic use of interface design to exploit cognitive weakness. The rent-to-own application is the same architecture built in paper and social pressure instead of pixels.

    Now compound it. The populations most likely to use rent-to-own — paycheck-to-paycheck cash flow, no traditional credit access, housing instability — are the populations whose cognitive bandwidth is most depleted at the moment the policy arrives. Mani et al. (2013) demonstrated that financial scarcity alone reduces available cognitive bandwidth by approximately 13 IQ points. Not intelligence. Bandwidth — the same resource that deliberative decision-making requires. The brain is already maxed out by the financial problem that brought the customer to the store. The privacy policy arrives in a system running on fumes.

    Then add shame. The application is a status exposure event — proving you deserve approval despite not having the credit to buy outright. Pausing to read the policy signals suspicion, delays the approval, extends the discomfort. The social pressure to just sign and move on is another cognitive tax stacked on top of the scarcity tax stacked on top of the design tax.

    The result: a poverty premium on consent.
    The less financial margin you have, the less cognitive margin you have to evaluate what you’re consenting to — and the more valuable your data is to the company extracting it. The system does not exploit everyone equally. It extracts the most from those who can afford to give the least.

    Which means “I Agree” is not agreement. Consent requires understanding the terms, having a genuine alternative, and deliberating under conditions that permit it. None of those conditions exist here. The reading burden is structurally impossible. The alternative to consenting is exclusion from the service. Cognitive load, edging itself with financial scarcity and social pressure, has shifted the decision from deliberative to heuristic before the policy is ever presented.

    Automatic consent makes you compliant. Informed consent brings reckoning.

    References

    Acquisti, A., Brandimarte, L., & Loewenstein, G. (2015). Privacy and human behavior in the age of information. Science, 347(6221), 509–514. https://doi.org/10.1126/science.aaa1465
    Ben-Shahar, O., & Schneider, C. E. (2014). More than you wanted to know: The failure of mandated disclosure. Princeton University Press.
    Brignull, H. (2023). Deceptive patterns: Exposing the tricks tech companies use to control you. Testimonium.
    Calo, R. (2014). Digital market manipulation. George Washington Law Review, 82(4), 995–1051.
    Kahneman, D. (2011). Thinking, fast and slow. Farrar, Straus and Giroux.
    Mani, A., Mullainathan, S., Shafir, E., & Zhao, J. (2013). Poverty impedes cognitive function. Science, 341(6149), 976–980. https://doi.org/10.1126/science.1238041
    McDonald, A. M., & Cranor, L. F. (2008). The cost of reading privacy policies. I/S: A Journal of Law and Policy for the Information Society, 4(3), 543–568.
    Microsoft Corporation. (2025, July 30). Microsoft Services Agreement. https://www.microsoft.com/en-us/servicesagreement/
    Solove, D. J. (2013). Introduction: Privacy self-management and the consent dilemma. Harvard Law Review, 126(7), 1880–1903.
    Thaler, R. H., & Sunstein, C. R. (2008). Nudge: Improving decisions about health, wealth, and happiness. Yale University Press

  • Predatory Privacy Policies

    Predatory Privacy Policies

    Literary Assistant = Multiple LLMs

    Can you tell between AI-generated text and Genuine Shit?


    Part 1: The Architecture of Extraction


    Why is renting expensive as fuck? Weekly payments cost more than the rental.

    This is the first installment of a three-part series examining how privacy policies operate inside the rent-to-own industry as a case study for a broader pattern in consumer finance. Part 1 maps the architecture: what data gets collected, where it goes, and what the “sharing” language in published policies actually authorizes.

    “TOO FUCKIN LONG; NOT GONNA READ!”

    If a business asks for your income, your residence history, your references, and a government ID scan to lease a couch, that paperwork is doing more than just approving. It is feeding a data ecosystem in which behavioral, financial, and identity information moves among vendors, marketers, fraud-prevention firms, and analytics partners in language that most policies never make legible. Read a privacy policy as part of the price tag — because in measurable economic terms, it is.

    What this post is (and isn’t)

    This is consumer education and structural commentary on industry patterns. It is not legal advice and does not accuse any specific company of violating any specific law. Where companies are referenced, they appear as examples of an industry-wide pattern, and any reader is encouraged to verify current practices by reading the company’s published privacy policy directly and noting the date of access.

    The Profitable as Fuck Risk Model // NO CREDIT NO PROBLEM!

    A subscription service collects an email address and a card number. A retail loyalty program collects a phone number. Rent-to-own operates on a more invasive, frequent-contact model: the business ships durable goods—appliances, electronics, furniture (bed bug-free!)—to the contract’s home in exchange for the promise of weekly, biweekly, or monthly payments over the term of the rental contract. The merchandise sits in the customer’s possession before the business has been paid in full. That inversion of typical retail risk is what licenses the application’s depth.
    A standard rent-to-own application typically requests, at minimum, a verifiable income source, stable and acceptable residence, multiple personal references at separate addresses (often heavily suggesting to include relatives because that shit’s going to efface their risk), an ID card of some sort, and the applicant’s date of birth and Social Security number for identity and credit verification (of course the credit is just to make sure that you’re not attempting fraud). Application flows mediated by mobile devices or in-store tablets often add device telemetry and, in some cases, biometric identifiers from ID-capture systems. Together, these constitute what privacy researchers describe as a high-resolution identity profile — far more diligent than the data captured by most consumer-facing services (Christl & Spiekermann, 2016).
    The customer experiences this collection as a source of friction: paperwork to be endured to take the merchandise home today. Merchandise that’s critical to furnishing a comfortable living space; Sofas, Television, Washer & Dryer, Fridge, Home Computer, a fuckin Bed, it’s expensive shit people desperately need (and not typically the kind of stuff one wants to collect off the side of the road…usually.)
    Each completed application produces a structured record that has utility well beyond the underwriting decision. The Federal Trade Commission’s foundational report on the data broker industry documented that …

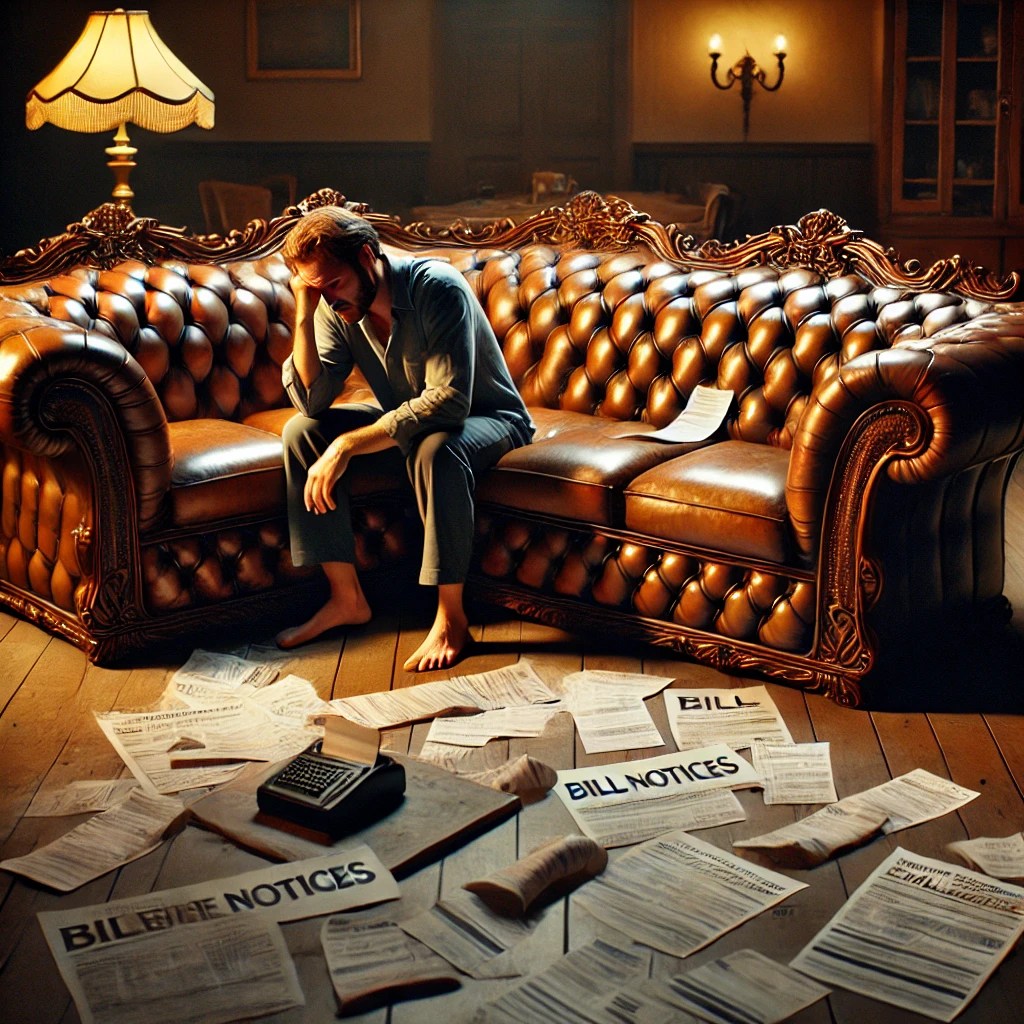
    A man sits despondently on a luxurious, tufted brown leather sectional sofa in a dimly lit room. He is leaning forward with his head down, barefoot, and dressed in simple grey loungework. The floor around him is cluttered with a typewriter and numerous scattered papers prominently labeled "BILL," "NOTICE," and "BILL NOTICES." The contrast between the opulent furniture and the overwhelming evidence of financial distress highlights a sense of irony and despair.

    …consumer-finance application data is among the most commercially valuable categories of personal information precisely because it links identity, location, employment, and financial behavior in a single verified record
    (Federal Trade Commission, 2014).


    Where Your Shit Actually Goes // “Vendors, Service Providers, Affiliates, and Partners”

    “Vendors, service providers, affiliates, and partners“— appear in nearly every rent-to-own privacy policy published today. It reads like nothing. It authorizes everything, so why not just say ”Everybody in the World?“because affiliates and partners are the critical factor, basically eliminating all the risk to lease expensive shit despite shit for credit.

    Because those affiliates and partners are going to really allow you and your lucky number of familial references the perfect opportunity to memorize what the different SPAM filters your devices support, because the affiliates and partners are partners that get a hard on for all of that precious Metadata you just provided about your current ’finally-financially-somewhat-stable-getting-back-on-your-feet-living-situation’ those FUCKS ‘Pimp Your Data’ out to the most annoying and relentless debt collection network that’s purchased your debt’s to pennies on the dollar, and paid a premium to the rent-to-own corporate headquarters to find your ass because they know where that shit credit goes to buy nice shit. This feels like a trap that became a recognizable pattern the second time this happened to me, when 5 years separated a binge of debt collection calls that would call the same older sister, annoyed as fuck that I wasn’t answering the debt collectors, because for some reason… she needed to have voicemail storage space and those 2-minute-long colorful voicemails accumulated quickly.
    Each word is a category containing dozens of companies the customer never identified, never contracted with, and will never audit.

    Cookies be makin’ my browser obese

    Service providers mean payment processors, cloud hosting providers, fraud-prevention vendors, and identity-verification services. Each has its own retention policy and downstream sharing arrangements. You can’t inspect any of them.
    Vendors and partners mean ad-tech infrastructure: retargeting platforms, email marketers, and the programmatic advertising auction operated by Google, Meta, TikTok, and adjacent companies. Your behavioral data enters that system and gets used to target you across thousands of unrelated sites. Rent-A-Center’s own published cookie disclosure names twelve advertising partners by name — including Meta, Google, TikTok, Pinterest, Yahoo, Microsoft Bing, Pandora, Zeta, AppNexus/Xandr, Verizon/Oath, Causal IQ, and Claritas (Upbound Group, Inc., 2025). Twelve companies are watching one rental application. Cookie Monsters Series coming down the pipeline!

    Nonexistent Entities Entitled Existence

    Affiliates mean corporate parent and subsidiary entities. For Rent-A-Center, that’s Upbound Group, Inc., and every current or future subsidiary under its umbrella. Their policy says it plainly: “all information gathered about you by the Company may be shared with any of the Company’s current or future subsidiaries or affiliates“(Upbound Group, Inc., 2025). Current or future. Entities that don’t exist yet already have authorization to receive your data. You signed one form to lease a couch. That sentence authorized data flow to every entity above, plus any entity that acquires the company after the fact.

    And here’s the one that should make you put your phone down for a second: the same policy discloses that in the event of “bankruptcy, insolvency, or dissolution proceedings,” your personal information may be shared with third parties as part of the sale or reorganization process (Upbound Group, Inc., 2025). If the company goes under, your data is an asset on the auction block. Imagine your bankrupt bullshit 420 credit score is the secret ingredient keeping a CEO’s Timeshare resort in Malaysia current with its Maintenance Fees.

    References

    Christl, W., & Spiekermann, S. (2016). Networks of control: A report on corporate surveillance, digital tracking, big data & privacy. Facultas.

    Federal Trade Commission. (2014). Data brokers: A call for transparency and accountability. https://www.ftc.gov/system/files/documents/reports/data-brokers-call-transparency-accountability-report-federal-trade-commission-may-2014/140527databrokerreport.pdf

    Upbound Group, Inc. (2025, January 1). Rent-A-Center privacy policy. https://www.rentacenter.com/privacy-policy [Accessed April 16, 2026]